Hello
I am reaching out to you because I have a case that I don’t know how to handle it.
I create several roles that I attach to teams or OIDC groups. In these roles, I add scopes to give access to given entities.
But I want to have some roles to be universal with, for example, a full ReadOnly role.
A role that have the READ permission for all current and future entities.
For now, the only possibility is to add READ permission for each entity individually, which is really not that handy when you have a lot of entities and we have to update the role with each new created entity.
So, my question is : how can I handle that ? And is it possible to add the ability to enter a wildcard in the scope field like so :
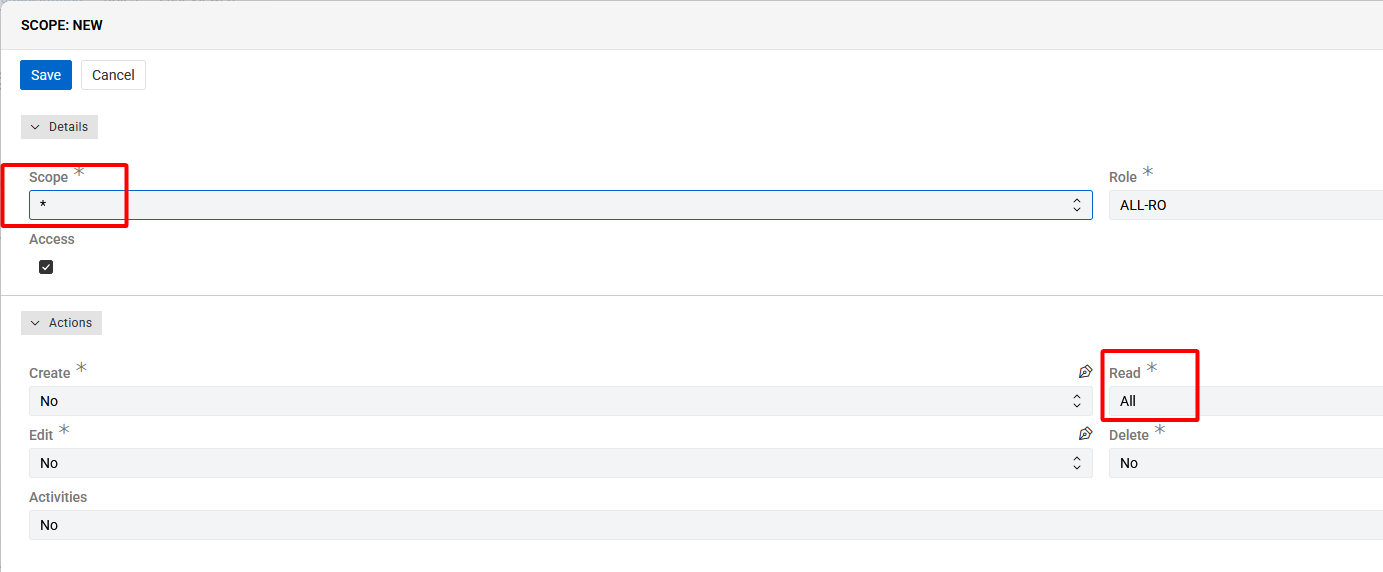
Or an (ALL) option, no matter the format.
Thank you for your help on this !